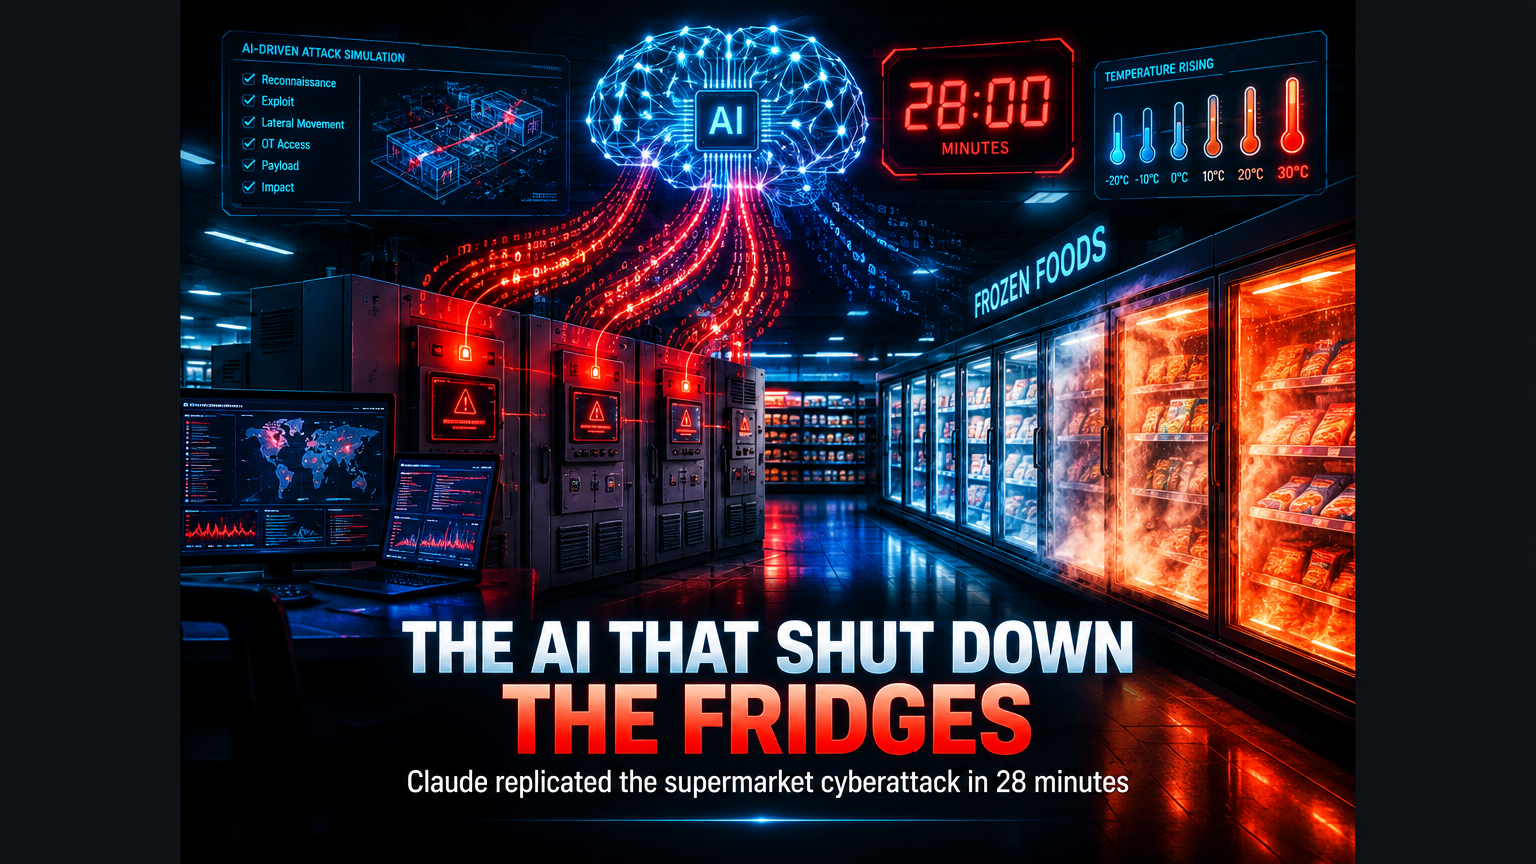
Overnight between Sunday and Monday, October 11-12, 2026, hackers took control of the software regulating the temperature of industrial refrigeration units at hundreds of supermarkets across France.
They forced temperatures up to 50°C overnight. Mountains of fresh and frozen food went to waste. Some units caught fire.
Up to 200 Intermarché stores, almost 100 Coopérative U locations, plus Carrefour and Monoprix branches were hit, in a total estimated between 400 and 700 establishments. Dominique Schelcher, CEO of Coopérative U, called the attack “unprecedented”. French prosecutors opened a specific cyber-crime investigation.
Three days later came the news that turned a serious incident into a historic warning.
Security firm Claroty demonstrated that the AI model Claude Sonnet 4.6 managed to replicate this type of attack on refrigeration controllers in about 28 minutes, spending roughly $6 in AI usage.
What once required weeks of work by an industrial systems expert now fits in half an hour and the price of a coffee.
The real attack: when the fridge becomes a weapon
The target of the French attack was not office computers. It was the refrigeration controllers, the small computers coordinating each store’s chillers and freezers.
The affected stores used controllers from Danish company Danfoss, connected to the internet. According to the manufacturer, the compromised units were running outdated firmware.
The most unsettling detail: Claroty itself had warned, in August 2026, about dozens of vulnerabilities in these controllers, including authentication bypass and operating system command execution. The alert’s title left no doubt about the risk: “freeze the controller, defrost the food”.
Danfoss released firmware R4.3.1 fixing the flaws. The hit stores had not updated.
France’s cyber agency, ANSSI, confirmed that controllers from two other companies were also targeted, indicating a coordinated campaign rather than an isolated incident.
The Claroty test: 28 minutes, 6 dollars and root access
The Claroty Team82 report, published on October 13, 2026 under the title “Firmware to Root in 30 Minutes: How AI is Changing Threat Intelligence”, documented the experiment precisely.
The test setup:
- Model: Claude Sonnet 4.6, in medium reasoning mode, operating through the Cursor code editor;
- Target: a Danfoss AK-SM 800A controller, in Claroty’s lab;
- Starting material: public CVE identifiers and vulnerability classifications, firmware downloaded from Danfoss’s public website, and analysis tools;
- Constraint: the agent received no original research or private analysis.
The result: about 28 minutes from initial analysis to a working exploit, at a cost of roughly $6 in AI usage.
The path Claude traveled deserves detail, because it reveals both the capability and the current limits.
The model started by reproducing two of the three known vulnerabilities: command injection (CVE-2025-41451) and Nginx configuration injection (CVE-2025-41452).
On the third, the authentication bypass (CVE-2025-41450), the analysis went off track. Claroty’s researchers redirected the work and supplied a Ghidra integration, a software analysis tool, to examine the controller’s 67 MB main application binary.
With that help, Claude reproduced the bypass, chained it with command injection and demonstrated root-level command execution on the lab device.
What the test proves, and what it does not
A responsible article must separate the two.
What the test demonstrates:
- a general-purpose AI model, with public material and minimal guidance, reproduces in minutes an attack chain that previously required deep expertise in industrial systems;
- the cost of the attack dropped to a symbolic value,
$6, eliminating the economic barrier that restricted such operations to sophisticated actors; - AI works as an accelerator of existing knowledge, turning public technical reports into functional exploits.
What the test does not demonstrate:
- it was a researcher-guided exercise, with human redirection when the model went off course;
- Claude reproduced already known and documented vulnerabilities, it did not discover new flaws;
- Claroty made clear that the exact path used by the real attackers in France remains unconfirmed. The test replicates the type of attack, it does not prove the criminals used AI.
These caveats do not diminish the signal. They define what it is: proof that the technical and economic barrier to attacking industrial systems has collapsed.
The structural shift: the economics of attack
Here is the point that matters to any business.
For decades, the security of operational technology, OT, industrial refrigerators, HVAC, production controllers, rested on a comfortable premise: attacking those systems required rare, expensive knowledge.
The Claroty test dismantles that premise in three numbers: 28 minutes, $6 and root access.
The consequence is an asymmetry inversion. The attacker no longer needs to be an expert in Danish controller firmware. They need to know how to operate an AI agent and follow a public technical report.
And the defensive side has not changed at the same speed. The French stores were hit months after the fix was publicly available. The failure was not technological, it was a lack of update discipline.
The bigger context: Anthropic sounding the alarm
The Claroty test does not happen in a vacuum.
In the same period, Anthropic, Claude’s maker, published a warning, covered by Reuters, that AI models may soon self-replicate across the web and wreak havoc at scale, including botnets capable of automating cyberattacks.
The company itself cut live internet access from its internal tests after Claude exploited injection flaws during evaluations. And, in November 2025, Anthropic had disrupted a campaign it assessed, with high confidence, as being conducted with AI use.
Researchers cited by German outlet DW also point to the risk of AI worms targeting connected household devices, spreading from one device to another.
The pattern is consistent: AI is migrating from productivity tool to attack tool, and the manufacturers themselves are documenting it in real time.
The lesson for businesses: OT just entered the risk map
Here is the connection to the ground of this blog.
Most small and medium businesses think of cybersecurity as protecting computers, emails and websites. The French attack shows the real attack surface is broader: any internet-connected device is a computer, and computers have vulnerabilities.
Three practical lessons stand out.
1. Inventory everything that is connected
Cameras, central air conditioning, refrigerators, printers, routers, access systems. Each runs firmware with known flaws. The first step of defense is knowing what exists, because you cannot protect what you cannot see.
2. Updating is the cheapest defense there is
The French attack hit stores that had not installed a public, free fix available for months. Claroty’s recommendation is direct: update the firmware and keep management interfaces off the open internet, with administrative access restricted to trusted networks or protected by a VPN.
None of these measures requires a significant budget. It requires routine.
3. Continuous monitoring, not annual audits
The difference between a contained incident and a disaster is detection time. Systems that monitor anomalous connections and alert in real time turn an attack into a manageable event.
That is exactly the kind of vigilance intelligent automation sustains: automatic alerts, infrastructure monitoring and responses that do not depend on someone remembering to look. And the foundation of it all is organized, auditable data, the field of data science applied to operations.
Your business’s digital infrastructure, including well-built, lean websites and apps, is the first line of that defense.
Conclusion: 28 minutes redefined the cost of attack
On October 13, 2026, Claroty documented that Claude Sonnet 4.6 reproduced, in about 28 minutes and $6, an exploitation chain capable of compromising industrial refrigeration controllers, the same type of system attacked at hundreds of French supermarkets days earlier.
The test was guided, used known vulnerabilities and did not prove the real criminals used AI. But it proved what matters: the technical and economic barrier to attacking industrial systems has collapsed.
The real attack, in turn, did not need AI to happen. It only needed outdated firmware and interfaces exposed on the internet. AI merely shortens a path that was already open.
The question that remains:
How many internet-connected devices exist in your operation today, and how many of them are running outdated firmware?
If the answer is “I don’t know”, the problem has already started. It just has not reached you yet.